1. 为防范国家数据安全风险、维护国家安全、保障公共利益,2021 年7月,中国网络安全审查办公 室发布公告,对“滴滴出行”、“运满满” 、“货车帮” 和“BOSS 直聘”开展网络安全审查。此次 审查依据的国家相关法律法规是(1) 。详情 ↗
- A.《中华人民共和国网络安全法》和《中华人民共和国国家安全法》
- B.《中华人民共和国网络安全法》和《中华人民共和国密码法》
- C.《中华人民共和国数据安全法》和《中华人民共和国网络安全法》
- D.《中华人民共和国数据安全法》和《中华大民共和国国家安全法》
1. 为防范国家数据安全风险、维护国家安全、保障公共利益,2021 年7月,中国网络安全审查办公 室发布公告,对“滴滴出行”、“运满满” 、“货车帮” 和“BOSS 直聘”开展网络安全审查。此次 审查依据的国家相关法律法规是(1) 。详情 ↗
2. Android 是开源的移动终端操作系统,共分成Linux 内核层、系统运行库层、应用程序框架层和应 用程序层四个部分,显示驱动位于(2) 。详情 ↗
3. 信息系统面临多种类型的网络安全威胁。其中,信息泄露是指信息被泄露或透露 给某个非授权的实体,(3) 是指数据被非授权地进行增删修改或破坏而受到损失;, (4) 是指对信息或 其他资源的合法访问被无条件地阻止 (5) 是指通过对系统进行长期监听,利用统计分析方法对诸如通 信频度、通信的信息流向、通信和总量的变化等参数进行研究,从而发现有价值的信息和规律。详情 ↗
4. 信息系统面临多种类型的网络安全威胁。其中,信息泄露是指信息被泄露或透露 给某个非授权的实体,(3) 是指数据被非授权地进行增删修改或破坏而受到损失;, (4) 是指对信息或 其他资源的合法访问被无条件地阻止 (5) 是指通过对系统进行长期监听,利用统计分析方法对诸如通 信频度、通信的信息流向、通信和总量的变化等参数进行研究,从而发现有价值的信息和规律。详情 ↗
5. 信息系统面临多种类型的网络安全威胁。其中,信息泄露是指信息被泄露或透露 给某个非授权的实体,(3) 是指数据被非授权地进行增删修改或破坏而受到损失;, (4) 是指对信息或 其他资源的合法访问被无条件地阻止 (5) 是指通过对系统进行长期监听,利用统计分析方法对诸如通 信频度、通信的信息流向、通信和总量的变化等参数进行研究,从而发现有价值的信息和规律。详情 ↗
6. 以下关于软件开发过程中增量模型优点的叙述中, 不正确的是(6) 。详情 ↗
7. 在 Python 语言中,(7) 是一种可变的、有序的序列结构,其中元素可以重复5详情 ↗
8. 在一个分布式软件系统中,一个构件失去了与另一个远程构件的连接。在系统修复后,连接于 30 秒之内恢复,系统可以重新正常工作直到其它故障发生。这一描述体现了软件系统的(8) 。详情 ↗
9. 在三层 C/S 软件架构中,(9) 是应用的用户接口部分,负责与应用逮辑间的对话功能,(10)是 应用的本体,负责具体的业务处理逻辑。详情 ↗
10. 在三层 C/S 软件架构中,(9) 是应用的用户接口部分,负责与应用逮辑间的对话功能,(10)是 应用的本体,负责具体的业务处理逻辑。详情 ↗
11. 以下关于以太网交换机转发表的叙述中,正确的是 (11) 。详情 ↗
12. 1000BASE-TX 采用的编码技术为 (12) 。详情 ↗
13. HDLC 协议通信过程如下图所示,其中属于1 帧的是 C13) 。详情 ↗
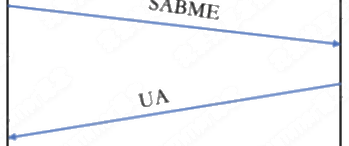
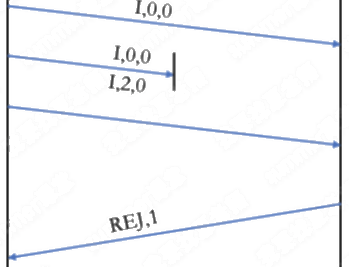
14. HDLC 协议中采用比特填充技术的目的是(14) 。详情 ↗
15. IPv4 首部的最大值为(15)字节,原因是 IHL 字段长度为(16) 比特。详情 ↗
16. IPv4 首部的最大值为(15)字节,原因是 IHL 字段长度为(16) 比特。详情 ↗
17. 由于采用了(17) 技术,ADSL SEATS BAT 1 ELS FP) A.详情 ↗
18. 以太网交换机中采用生成树算法是为了解决(18) 问题。详情 ↗
19. 6 个速率为 64Kb/s 的用户按照统计时分多路复用技术(STDM) 复用到一条干线上、若每个用户平均 效率为 80%,王线开销 4%,则干线速率为(19) Kb/s.详情 ↗
20. Internet 网络核心采取的交换方式为(20) 。详情 ↗
21. 以下关于虚电路交换技术的叙述中,错误的是(21) 。详情 ↗
22. SDH 的帧结构包含(22) 。详情 ↗
23. 假设客户端采用持久型 HTTP 1. 1 版本向服务器请求一个包含 10 个图片的网页。设计页面传输时 间为Tbas,图片传输的平均时间为Timg,客户端到服务器之间的往返时间为 RIT,则从客户端请求开 始到完整取回该网页所需时间为(23) 。详情 ↗
24. fECSMA/CD 中,同一个冲突域中的主机连续经过 3 次冲突后,每个站点在接下来信道空闲的时候 立即传输的概率是(24) 。详情 ↗
25. 在下图所示的网络拓扑中,假设自治系统 AS3 和AS2 内部运行08PF,AS1 和 AS4 内部运行RIP。 各自治系统间用 BGP 作为路由协议,并假设AS2 和AS4 之间没有物理链路。则路由器 3c 基于(25)协 议学习到网络 x 的可达性信息。1d 通过(26) 学习到 x 的可达性信息。 人 2本关 & a 人 ® & 信 > 7详情 ↗
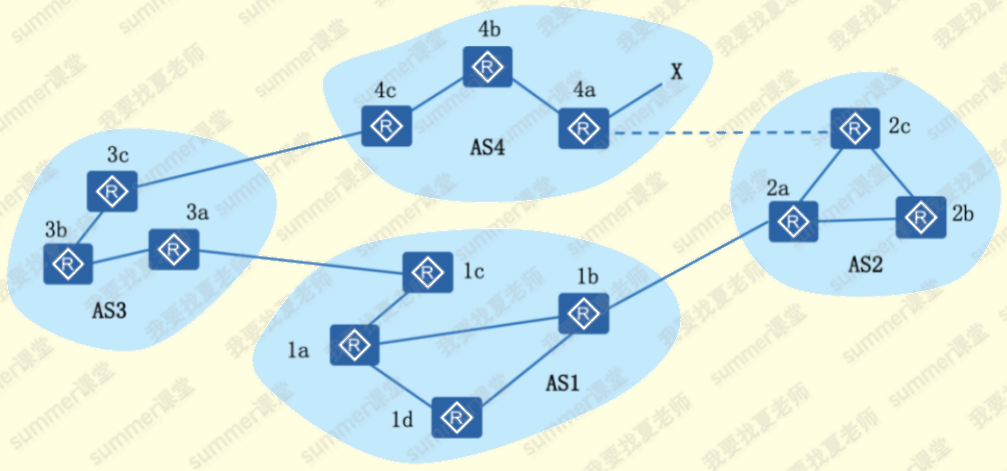
26. 在下图所示的网络拓扑中,假设自治系统 AS3 和AS2 内部运行08PF,AS1 和 AS4 内部运行RIP。 各自治系统间用 BGP 作为路由协议,并假设AS2 和AS4 之间没有物理链路。则路由器 3c 基于(25)协 议学习到网络 x 的可达性信息。1d 通过(26) 学习到 x 的可达性信息。 人 2本关 & a 人 ® & 信 > 7详情 ↗
27. Traceroute 在进行路由追踪时发出的 ICMP 消息 (27) ,收到的消息是中间节点或目的节点返回 的(28) 。详情 ↗
28. Traceroute 在进行路由追踪时发出的 ICMP 消息 (27) ,收到的消息是中间节点或目的节点返回 的(28) 。详情 ↗
29. 下列不属于快速 UDP 互联网连接(QUIC) 协议的优势是(29) 。详情 ↗
30. 对于链路状态路由算法而言,若共有N 个路由器,路由器之间共有M条链路,则链路状态通告的 消息复杂度以及接下来算法执行的时间复杂度分别是(30) 。详情 ↗
31. 距离向量路由协议所采用的核心算法是(31)。详情 ↗
32. IPv4 报文分片和重组分别发生在 (32) 。详情 ↗
33. 下图为某网络拓扑的片段,将 1 和 2 两条链路聚合成链路 61,并与链路 3 形成VRRP 主备关系, 管理员发现在链路 2 出现 CRC 错误告警,此时该网络区域可能会发生的现象是 (33) 。 一人 一> <生> <和> EHO 3 c VRRP 3详情 ↗
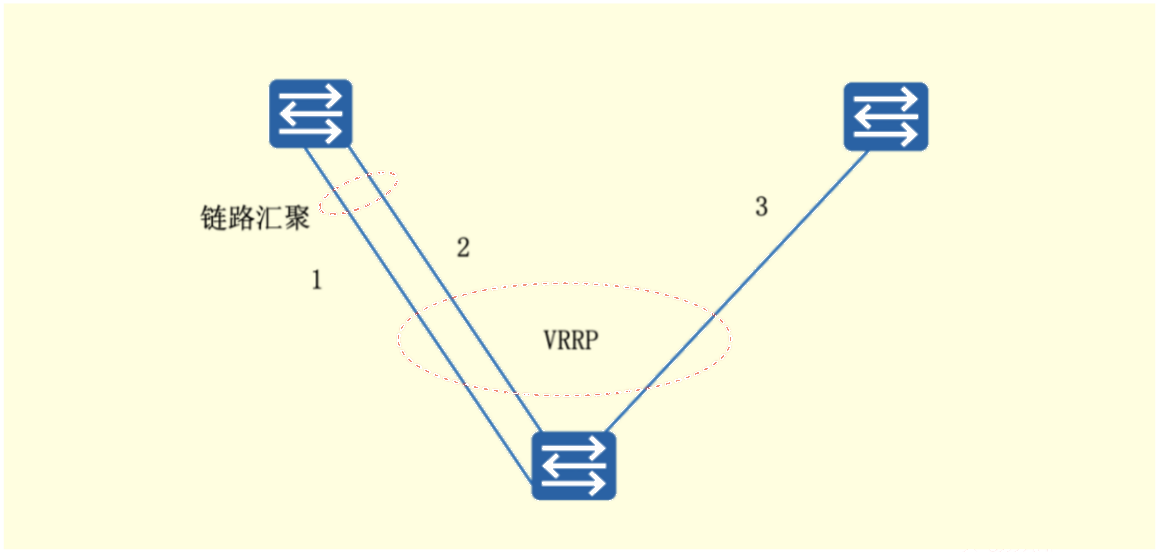
34. 若循环冗余校验码 CRC 的生成器为 10111,则对于数据10100010000 计算的校验码应为(34) 。 该 CRC 校验码能够检测出的突发错误不超过(35) 。详情 ↗
35. 若循环冗余校验码 CRC 的生成器为 10111,则对于数据10100010000 计算的校验码应为(34) 。 该 CRC 校验码能够检测出的突发错误不超过(35) 。详情 ↗
36. (36) 子系统是楼宇布线的组成部分。详情 ↗
37. 客户端通过DHCP 获得 TP 地址的顺序正确的是(37) 。 OX Psy RIX DHCP REQUEST 请求 IP 地址 QSERVER AIX DHCP OFFER 报文响应 @¥ Pitti RIE DHCP DISCOVER 报文寻找 DHCP SERVER @SERVER 收到请求后回应 ACK 响应请求详情 ↗
38. 某高校计划采用扁平化的网络结构。为了限制广播域、解决 YLAN 资源紧缺的问题,学校计划采 FA QinQ (802. 1Q-in-802. 1Q) 技术对接入层网络进行端口隔离。以下关于 Qing 技术的叙述中,错误的 是(38) 。详情 ↗
39. 下面支持 IPv6 的是 (39) 。详情 ↗
40. 以下关于 OSPF 特性的叙述中,错误的是(40) 。详情 ↗
41. 策略路由通常不支持根据 (41)来指定数据包转发策略。详情 ↗
42. SDN 的网络架构中不包含(42) 。详情 ↗
43. 窃取是一种针对数据或系统的(43) MB. DDoS 攻击可以破坏数据或系统的(44) 。详情 ↗
44. 窃取是一种针对数据或系统的(43) MB. DDoS 攻击可以破坏数据或系统的(44) 。详情 ↗
45. 以下关于 IPSec 的说法中,错误的是(45) 。详情 ↗
46. 是由我国自主研发的无线网络安全协议。详情 ↗
47. FE Web 网站向 CA 申请了数字证书.用户登录过程中可通过验证 (47) 确认该证书的有效性, 以(48) 。详情 ↗
48. FE Web 网站向 CA 申请了数字证书.用户登录过程中可通过验证 (47) 确认该证书的有效性, 以(48) 。详情 ↗
49. 某公司要求数据备份周期为7 天,考虑到数据恢复的时间效率,需采用 (49) 备略。详情 ↗
50. 某网站的域名是 www. xyz. com,使用 SSL 安全页面,用户可以使用(50) 访问该网站。详情 ↗
51. 以下关于链路加密的说法中,错误的是(51) 。详情 ↗
52. 在运行 OSPF 的路由器中;可以使用(52) 命令查看 OSPF 进程下路由计算的统计信息,使用(53) 命令查看 OSPF 邻居状态信息。详情 ↗
53. 在运行 OSPF 的路由器中;可以使用(52) 命令查看 OSPF 进程下路由计算的统计信息,使用(53) 命令查看 OSPF 邻居状态信息。详情 ↗
54. DAR RF IPv6 地址的说法中,错误的是(54) 。详情 ↗
55. 在 IPv6 中,(55) 首部是每个中间路由器都需要处理的。详情 ↗
56. 在 GPON 中,上行链路采用(56) 的方式传输数据。详情 ↗
57. ZEPON 中,上行传输波长为 (57)nm。详情 ↗
58. 某居民小区采用 FTTB+HGW 网络组网,通常情况下,网络中的 (58) 部署在汇聚机房。详情 ↗
59. 以下关于光功率计的功能的说法中,错误的是(59) 。详情 ↗
60. 8 He 3006 的硬盘做 RAIDS 后的容量是(60) RAIDS 最多可以损坏 (61) 块硬极而不丢失数据。详情 ↗
61. 8 He 3006 的硬盘做 RAIDS 后的容量是(60) RAIDS 最多可以损坏 (61) 块硬极而不丢失数据。详情 ↗
62. 在无线网络中,通过射频资源管理可以配置的任务不包括(62) 。详情 ↗
63. 在无线网络中,天线最基本的属性不包括(63) 。详情 ↗
64. 下列路由表的概要信息中,迭代路由是(64),不同的静态路由有(65)条。详情 ↗
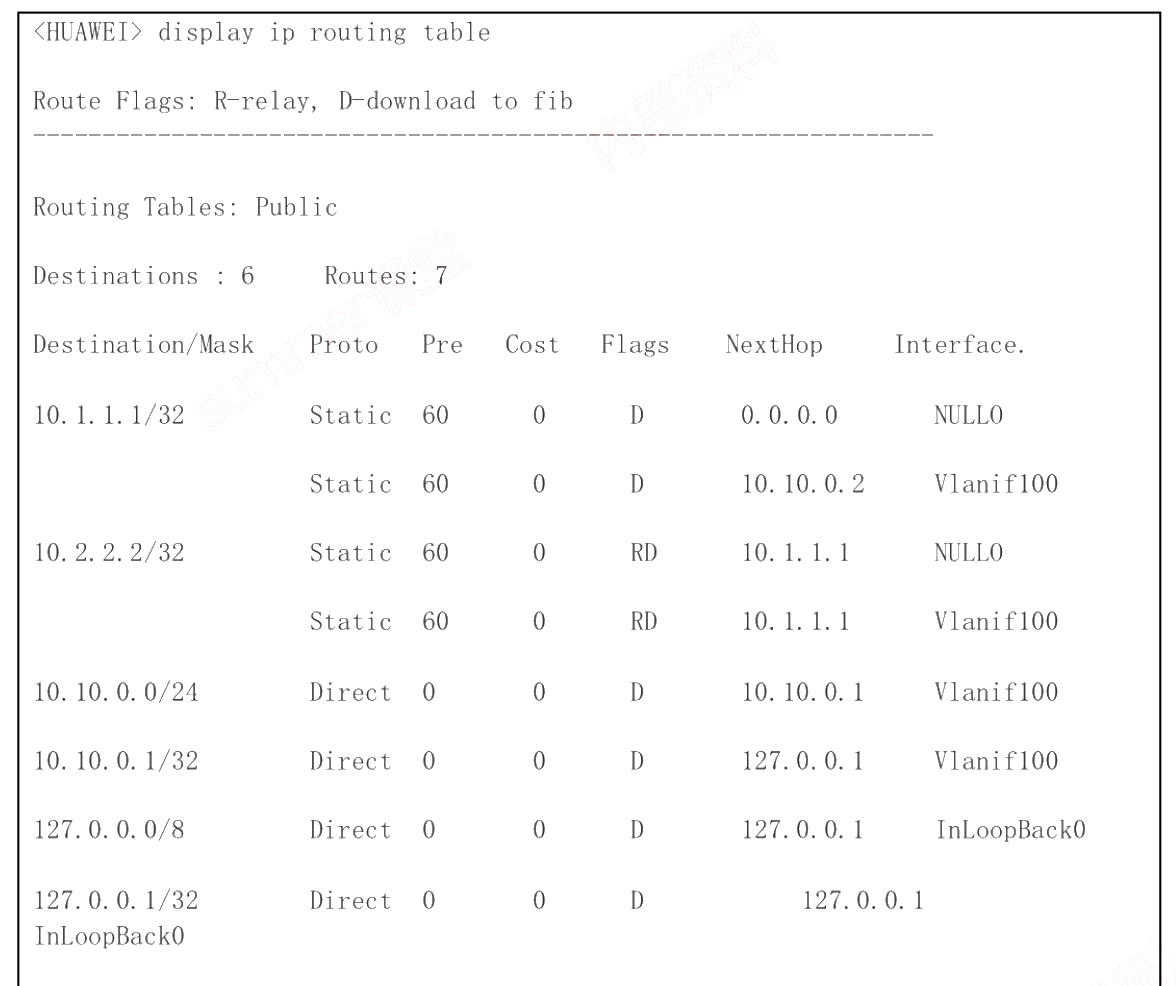
65. 下列路由表的概要信息中,迭代路由是(64),不同的静态路由有(65)条。详情 ↗
66. 下列命令片段用于配置(66)。<HUAWEI> system-view [HUAWEI] interface 10ge1/0/1 [HUAWEI-10GE1/0/1] loopback-detect enable [HUAWEI-10GE1/0/1] commit详情 ↗
67. 某主机可以 ping 通本机地址”而无法 ping 通网关地址,网络配置如下图所示,造成该故障的原 因可能是(67) 。详情 ↗
68. 某分公司财务 PC 通过专网与总部财务系统连接,拓扑如下图所示。某天,财务 PC 访问总部 财务系统速度缓慢、时断时好,网络管理员在财务 PC 端 ping 总部财务系统,发现有网络丢包,在光 电转换器 1 处 ping 总部财务系统网络丢包症状同上,在专网接入终端处ping 总部财务系统,网络延 时正常无于包,光纤 1 两端测得光衰为-28dBm,光电转换器 1 和 2 指示灯绿色闪烁。初步判断该故障 原因可能是(68) ,可采用(69) 措施较为合理。 分公司 ee oe | fi 双绞线1 | 光纤1 34) RBA im} | ‘eer fi | | baa 光电转换器1 光电转换器2 。 专网接入终端 。 ; 。 总部财务系统详情 ↗
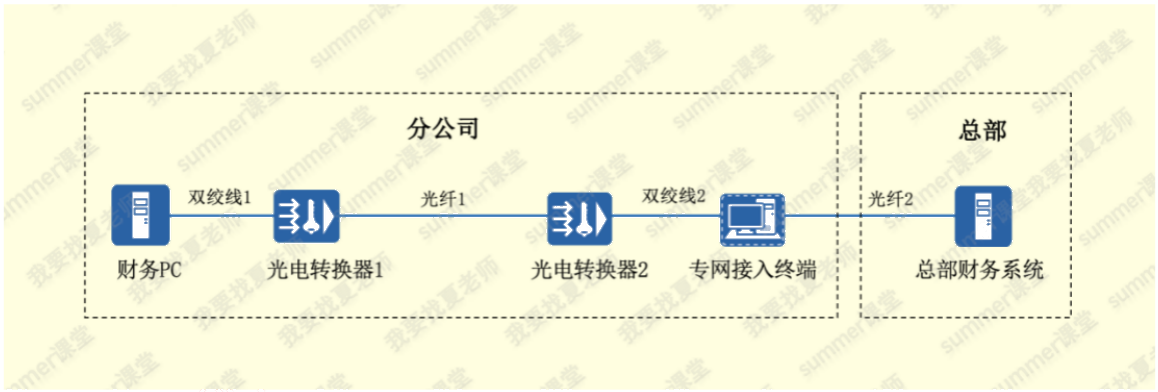
69. 某分公司财务 PC 通过专网与总部财务系统连接,拓扑如下图所示。某天,财务 PC 访问总部 财务系统速度缓慢、时断时好,网络管理员在财务 PC 端 ping 总部财务系统,发现有网络丢包,在光 电转换器 1 处 ping 总部财务系统网络丢包症状同上,在专网接入终端处ping 总部财务系统,网络延 时正常无于包,光纤 1 两端测得光衰为-28dBm,光电转换器 1 和 2 指示灯绿色闪烁。初步判断该故障 原因可能是(68) ,可采用(69) 措施较为合理。 分公司 ee oe | fi 双绞线1 | 光纤1 34) RBA im} | ‘eer fi | | baa 光电转换器1 光电转换器2 。 专网接入终端 。 ; 。 总部财务系统详情 ↗
70. 以下关于项目风险管理的说法中,不正确的是(70) 。详情 ↗
71. Data security is the practice of protecting digital information from (71) access, corruption, or theft throughout its entire lifecycle. It is a concept that encompasses every aspect of information security from the (72) security of hardware and storage devices to administrative and access controls, as well as the logical security of software applications. It also includes organizational (73) and procedures. Data security involves deploying tools and technologies that enhance the organization’ s Visibility into where its critical data resides and how itis used. These tools and technologies should (74) the growing challenges inherent in securing today’s complex distributed, hybrid, and/or multicloud computing environments. Ideally, these tools should be able to apply protections like (75) , data masking, and redaction of sensitive files, and should automate reporting to streamline audits and adhering to regulatory requirements.详情 ↗
72. Data security is the practice of protecting digital information from (71) access, corruption, or theft throughout its entire lifecycle. It is a concept that encompasses every aspect of information security from the (72) security of hardware and storage devices to administrative and access controls, as well as the logical security of software applications. It also includes organizational (73) and procedures. Data security involves deploying tools and technologies that enhance the organization’ s Visibility into where its critical data resides and how itis used. These tools and technologies should (74) the growing challenges inherent in securing today’s complex distributed, hybrid, and/or multicloud computing environments. Ideally, these tools should be able to apply protections like (75) , data masking, and redaction of sensitive files, and should automate reporting to streamline audits and adhering to regulatory requirements.详情 ↗
73. Data security is the practice of protecting digital information from (71) access, corruption, or theft throughout its entire lifecycle. It is a concept that encompasses every aspect of information security from the (72) security of hardware and storage devices to administrative and access controls, as well as the logical security of software applications. It also includes organizational (73) and procedures. Data security involves deploying tools and technologies that enhance the organization’ s Visibility into where its critical data resides and how itis used. These tools and technologies should (74) the growing challenges inherent in securing today’s complex distributed, hybrid, and/or multicloud computing environments. Ideally, these tools should be able to apply protections like (75) , data masking, and redaction of sensitive files, and should automate reporting to streamline audits and adhering to regulatory requirements.详情 ↗
74. Data security is the practice of protecting digital information from (71) access, corruption, or theft throughout its entire lifecycle. It is a concept that encompasses every aspect of information security from the (72) security of hardware and storage devices to administrative and access controls, as well as the logical security of software applications. It also includes organizational (73) and procedures. Data security involves deploying tools and technologies that enhance the organization’ s Visibility into where its critical data resides and how itis used. These tools and technologies should (74) the growing challenges inherent in securing today’s complex distributed, hybrid, and/or multicloud computing environments. Ideally, these tools should be able to apply protections like (75) , data masking, and redaction of sensitive files, and should automate reporting to streamline audits and adhering to regulatory requirements.详情 ↗
75. Data security is the practice of protecting digital information from (71) access, corruption, or theft throughout its entire lifecycle. It is a concept that encompasses every aspect of information security from the (72) security of hardware and storage devices to administrative and access controls, as well as the logical security of software applications. It also includes organizational (73) and procedures. Data security involves deploying tools and technologies that enhance the organization’ s Visibility into where its critical data resides and how itis used. These tools and technologies should (74) the growing challenges inherent in securing today’s complex distributed, hybrid, and/or multicloud computing environments. Ideally, these tools should be able to apply protections like (75) , data masking, and redaction of sensitive files, and should automate reporting to streamline audits and adhering to regulatory requirements.详情 ↗