1. 在支持多线程的操作系统中,假设进程 P 创建了线程TL、T2 和1T3,那么下列说法中,正确的是 (1) 。详情 ↗
- A.该进程中已打开的文件是不能被TI、T2 和 T3 共享的
- B.线程T1、T2 可以共享 P 进程中 T3 的栈指针
- C.线程T1、T2 和 T3 可以共享进程 P 打开的文件
- D.线程TL1、T2 和 T3 可以共享进程 P 的全局变量
1. 在支持多线程的操作系统中,假设进程 P 创建了线程TL、T2 和1T3,那么下列说法中,正确的是 (1) 。详情 ↗
2. 假设某计算机的字长为 32 位,该计算机文件管理系统磁盘空间管理采用位示图,记录磁盘的使用 情况,若磁盘的容量为 3006B,物理块的大小为 QIB,那么位示图的大小为 (2) 字。详情 ↗
3. 微内核,描述不正确的是 (3) 。详情 ↗
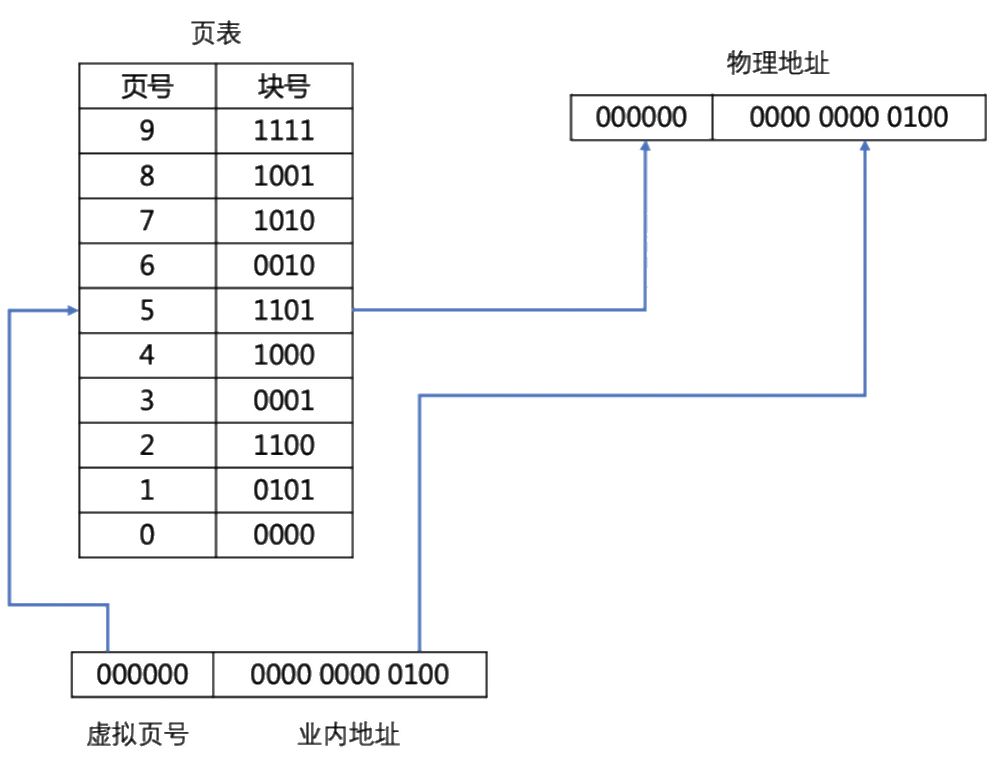
4. 分页内存管理的核心是将虚拟内存空间和物理内存空间皆划分为大小相同的页面,并以页面作为内存空间的最小分配单位,下图给出了内存管理单元的虚拟地址到物理页面翻译过程,假设页面大小为 4KB,那么 CPU 发出虚拟地址 0010 0000 0000 1000,访问的物理地址是(4)。详情 ↗
5. 以下关于计算机内存管理的描述中, (5) 属于段页式内存管理的描述。详情 ↗
6. 软件文档可分为用户文档和 (6 ) ,其中用户文档主要描述 (7) 和使用方法。详情 ↗
7. 软件文档可分为用户文档和 (6 ) ,其中用户文档主要描述 (7) 和使用方法。详情 ↗
8. 以下关于敏捷开发方法特点的叙述中,错误的是.8) 。详情 ↗
9. 某厂生产某种电视机,销售价为每台 2500 元,去年的总销售量为 25000 台,固定成本总额为 250 万元,可变成本总额为 4000 万元,税率为 1%,则该产品年销售量的怖亏平衡点为 (9) a, CAA (GREEN TARA.详情 ↗
10. 按照我国著作权法的权力保护期, (10) 受到永久保护。详情 ↗
11. 在 ADSL 接入网中通常采用离散多音频 CMT) 技术,以下关于 DMT 的叙述中,正确的是 (11) 。详情 ↗
12. 按照同步光纤网传输标准 (SONET ) ,0C-3 的数据速率为12) Mb/s.详情 ↗
13. 光纤传输测试指标中,回波损耗是指 C13) 。详情 ↗
14. 以 100Mb/s 以太网连接的站点A和B 相距 2000m,通过停等机制进行数据传输,传播速度为 200m/us,最高的有效传输速率为(14) 。详情 ↗
15. 下面是 LOOBASE-TX 标准中 MLT-3 编码的波形,出错的是第 C15) 位,传送的信息编码为 (16) +5V 1 | 上 了 |一sr Lot aa ee a a a i a详情 ↗
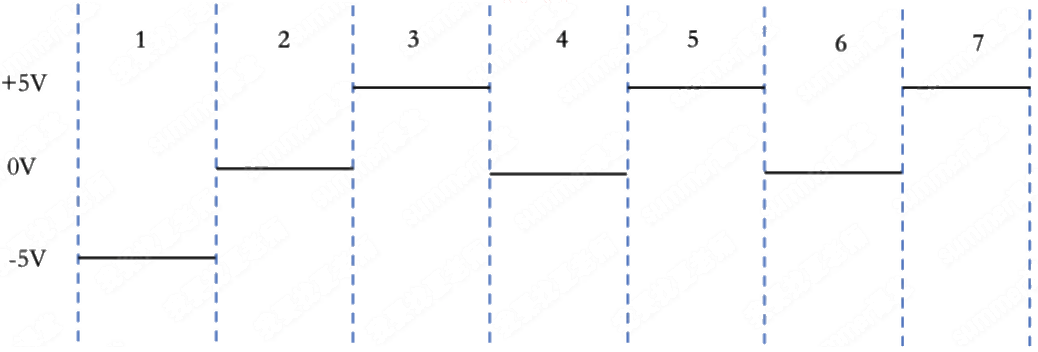
16. 下面是 LOOBASE-TX 标准中 MLT-3 编码的波形,出错的是第 C15) 位,传送的信息编码为 (16) +5V 1 | 上 了 |一sr Lot aa ee a a a i a详情 ↗
17. 以下关于HDLC 协议的叙述中错误的是 (17) 。详情 ↗
18. 以下关于 1000Base-T 的叙述中,错误的是(18) 。详情 ↗
19. 6 个速率为 64Kbys 的用户按照同步时分多路复用技术(TDM) 复用到一条干线上,若每个用户平 Ly BERN 80%, “FEI 4%, “FREE (19) Kb/s.详情 ↗
20. MIMO 技术在 56 中起着关键作用,以下不属于 MIMO 功能的是 (20) 。详情 ↗
21. 以下关于区块链系统“挖矿”行为的描述中,错误的是 (21) 。详情 ↗
22. 广城网可以提供面向连接和无连接两种服务模式,对应于两种服务模式,广城网有虚电路和数据 报两种传输方式,以下关于虚电路和数据报的叙述中,错误的是 (22) 。详情 ↗
23. 在光纤通信中,WDM 实际上是 (23)详情 ↗
24. 在Linux 中,DNS 的配置文件是 24) ,它包含了主机的域名搜索顺序和 DNS 服务器的地址。详情 ↗
25. 假设 CDMA 发送方在连续两个时隙发出的编码为 +l+l+l-1+l-1-1-1-1-1-1+1-1+1+1+1,发送方码片序列为+1+l+l-1+l-1-1-1,则接收方解码后的数据 应为 (25) 。详情 ↗
26. 对下面4个网络,110. 125. 129. 0/24、110. 125. 130. 0/24、110. 125. 132. 0/24 和 110. 125. 133. 0/24 进行路由汇聚,能覆盖这 4个网络的地址是 (26) 。详情 ↗
27. 在命令提示符中执行 ping ww. xy. com,所得结果如下图所示,根据TTL 值可初步判断服务器 182. 24. 21. 58 操作系统的类型是 27) 。其距离执行 bing 命令的主机有 (28) BE. 正在Ping ww. xy. com[182. 24. 21. 58]具有 32 字节的数据 来自180. 101. 49. 12 的回复: 字节=32 时间=4ms TTL=50 来自180. 101. 49. 12 的回复: 字节=32 时间=4ms TTL=50 来自180. 101. 49. 12 的回复: 字节=32 时间=4ms TTL=50 来自180. 101. 49. 12 的回复: 字节=32 时间=4ms TTL=50 182. 24. 21. 58 的 Ping 统计信息: 数据包: 已发送=4,已接收=4,丢失=0 (0%技失) , 往退行程的估计时间 《以毫秒为单位) : 最短=20ms,最长= 20ms,平均= 20ms详情 ↗
28. 在命令提示符中执行 ping ww. xy. com,所得结果如下图所示,根据TTL 值可初步判断服务器 182. 24. 21. 58 操作系统的类型是 27) 。其距离执行 bing 命令的主机有 (28) BE. 正在Ping ww. xy. com[182. 24. 21. 58]具有 32 字节的数据 来自180. 101. 49. 12 的回复: 字节=32 时间=4ms TTL=50 来自180. 101. 49. 12 的回复: 字节=32 时间=4ms TTL=50 来自180. 101. 49. 12 的回复: 字节=32 时间=4ms TTL=50 来自180. 101. 49. 12 的回复: 字节=32 时间=4ms TTL=50 182. 24. 21. 58 的 Ping 统计信息: 数据包: 已发送=4,已接收=4,丢失=0 (0%技失) , 往退行程的估计时间 《以毫秒为单位) : 最短=20ms,最长= 20ms,平均= 20ms详情 ↗
29. 下列哪种 BGP 属性不会随着 BGP 的 Update 报文通告给邻居? (29)详情 ↗
30. 一个由多个路由器相互连接构成的拓扑图如下所示,图中数字表示路由之间链路的费用,OSPF 路由协议将利用(30)算法计算出路由器 u 到 z 的最短路径费用值为(31)。详情 ↗
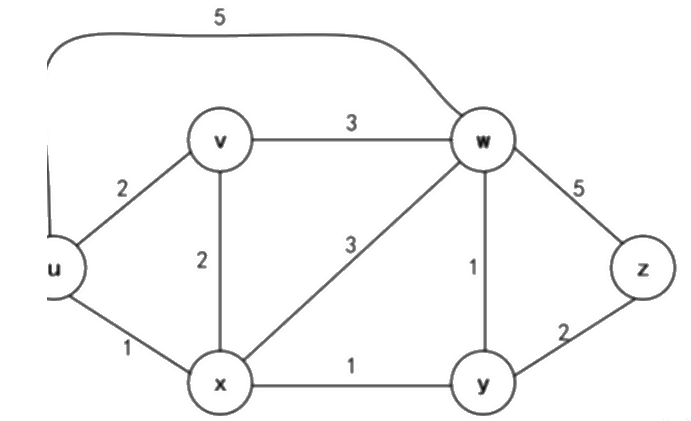
31. 一个由多个路由器相互连接构成的拓扑图如下所示,图中数字表示路由之间链路的费用,OSPF 路由协议将利用(30)算法计算出路由器 u 到 z 的最短路径费用值为(31)。详情 ↗
32. RIP 路由协议规定在邻居之间每 30 秒进行一次路由更新,如果 (32) 仍未收到邻居的通告消息, 则可以判断与其邻居路由器间的链路已经断开。详情 ↗
33. 假设一个了数据段的长度为 4000B8,要经过一段 MTU 为 1500B 的链路,该 IP 数据报必须经过分 片才能通过该链路,以下关于分片的叙述中,正确的是 (33) 。详情 ↗
34. 下图为某 Windows 主机执行 tracert www.xx.com 命令的结果。其中第 13 跳返回信息为"*",且地址信息为 request timed out,出现这种问题的原因可排除(34)。 C:\Users\Administrator>tracert www.xx.com 通过最多 30 个跃点跟踪 到 www.xx.com [103.224.182.246] 的路由: 1 <1 毫秒 <1 毫秒 <1 毫秒 162.118.1.1 2 1 ms 1 ms 1 ms 170.18.128.1 3 2 ms 2 ms 2 ms 183.214.254.9 4 2 ms 1 ms 1 ms 111.23.187.89 5 2 ms 1 ms 2 ms 111.24.9.169 6 22 ms 22 ms 22 ms 111.24.4.209 7 37 ms 80 ms 19 ms 221.183.68.141 8 25 ms 30 ms 25 ms 221.183.25.117 9 19 ms 21 ms 19 ms 221.183.55.81 10 185 ms 185 ms 185 ms 223.120.12.105 11 198 ms 198 ms 198 ms 223.120.6.126 12 283 ms 282 ms 286 ms 223.120.6.218 13 * * * request timed out 14 273 ms 272 ms 276 ms 213.1.2.3详情 ↗
35. 下图为某 UDP 报文的两个 16 比特,计算得到的 Internet Checksum 是(35)。 1110011001100110 1101010101010101详情 ↗
36. 假设主机 A 通过 Telnet 连接了主机 B,连接建立后,在命令行输入"C"。如图所示,主机 B 收到字符"C"后,用于运输回送消息的 TCP 段的序列号 seq 应为(36),而确认号 ack 应为(37)。详情 ↗
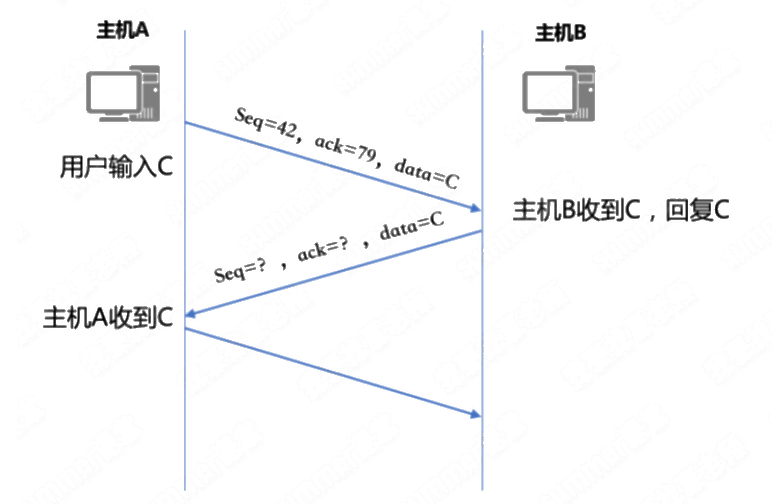
37. 假设主机 A 通过 Telnet 连接了主机 B,连接建立后,在命令行输入"C"。如图所示,主机 B 收到字符"C"后,用于运输回送消息的 TCP 段的序列号 seq 应为(36),而确认号 ack 应为(37)。详情 ↗
38. TCP 可靠传输机制为确定超时计时器的值,首先要估算 RTT,估算 RIT 采用如下公式,RTTs= (1- a) 半(估算 RTTs) tax GP RIT 样本) ,其中 a 的值取为 (38) 。详情 ↗
39. SYN Flooding 攻击的原理是 (39) 。 A AF TCP 三次握手,恶意造成大量 TCP 半连接,耗尽服务器资源,导致系统的拒绝服务 B. 有些操作系统在实现 TCPVIP 协议栈时,不能很好地处理 TCP 报文的序列号的查找问题,导致系统 Jatt C. 有些操作系统在实现 TCP/IP 协议栈时,不能很好地处理 IP} EAL, SRR CHT D. 有些操作系统协议栈在处理 IP 分片时,对于重组后超大的 IP 数据报不能很好地处理,导致缓存游 出而系统月省详情 ↗
40. 某Windows 主机网卡的连接名为“local“,下列命令中用于配置缺省路由的是 (40) 。详情 ↗
41. RA B/S 架构设计的某图书馆在线查询阅览系统,终端数量为 400 台,下列配置设计合理的是 (41) 。详情 ↗
42. 以下关于延迟的说法中,正确的是 (42) 。详情 ↗
43. (43) 不属于 IS07498-2 标准规定的五大安全服务。详情 ↗
44. 能够增强和提高网际层安全的协议是 (44) 。详情 ↗
45. 以下关于 Kerberos 认证的说法中,错误的是(457 。详情 ↗
46. 在 PKI 体系中,负责验证用户身份的是46) , (47) 用户不能够在 PKI 体系中申请数字证 书。详情 ↗
47. 在 PKI 体系中,负责验证用户身份的是46) , (47) 用户不能够在 PKI 体系中申请数字证 书。详情 ↗
48. PDR 模型是最早体现主动防御思想的一种网络安全模型,包括 (48) 3 个部分。详情 ↗
49. 两台运行在 PPP 链路上的路由器配置了 OSPF 单区域,当这两台路由器的 RouterID 设置相同时, (49) 。详情 ↗
50. 管理员无法通过 telnet 来管理路由器,下列故障原因中不可能的是 (50) 。详情 ↗
51. PPP 是一种数据链路层协议,其协商报文中用于检测链路是否发生自环的参数是 (51) 。详情 ↗
52. 以下关于RIP 路由协议与 0SPP 路由协议的描述中,错误的是 (52) 。详情 ↗
53. 以下关于 OSPF 协议路由聚合的描述中,正确的是 (53)详情 ↗
54. 在 Windows 系统中,默认权限最低的用户组是 (54) 。详情 ↗
55. 在 Linux 系统中,保存密码口令及其变动信息的文件是 (55) 。详情 ↗
56. EPON 可以利用 (56) 定位 OLT 到 ONU 段的故障。详情 ↗
57. 以下关于单模光纤与多模光纤区别的描述中,错误的是 (57) 。详情 ↗
58. 每一个光纤通道节点至少包含一个硬件端口,按照端口支持的协议标准有不同类型的端口,其中 NL-PORT 是 (58) 。详情 ↗
59. 光纤通信提供了三种不同的拓扑结构,在光纤交换拓扑中,N_PORT 端口通过相关链路连接至 (59) 。详情 ↗
60. 企业级路由器的初始配置文件通常保存在 (60) 上。详情 ↗
61. RAIDL 中的数据冗余通过(61) 技术实现的;详情 ↗
62. 在 IEEE802. 11 WLAN 标准中,频率范围在 5. 15-5. 35GHz 的是 (62) 。详情 ↗
63. 在进行室外无线分布系统规划时,菲涅尔区的因素影响在 (63) 方面,是一个重要的指标。详情 ↗
64. 检查设备单板温度显示如下图所示,对单板温度正常的判断是(64),如果单板温度异常,首先应该检查(65)。详情 ↗
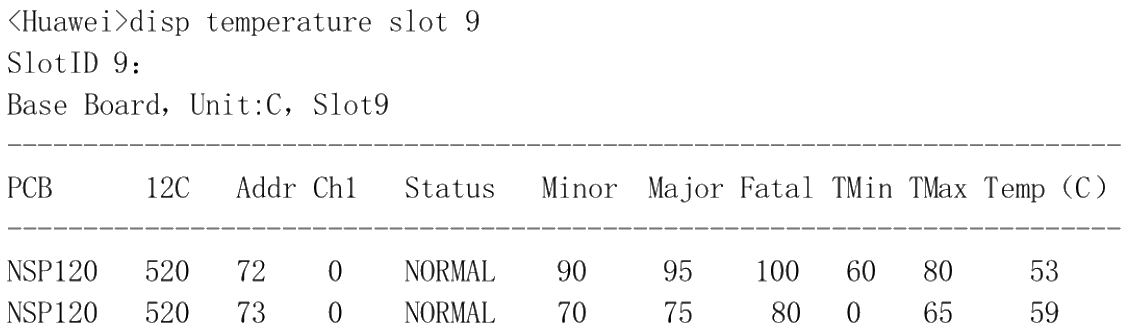
65. 检查设备单板温度显示如下图所示,对单板温度正常的判断是(64),如果单板温度异常,首先应该检查(65)。详情 ↗
66. 在华为VRP 平台上,直连路由、OSPF、RIP、静态路由按照优先级从高到低的排序是 (66) 。详情 ↗
67. 网络管理员检测到局域网内计算机的传输速度变得很慢,可能出现该故障的原因有(67)。①网络线路介质故障 ②计算机网卡故障 ③蠕虫病毒 ④WannaCry勒索病毒 ⑤运营商互联网接入故障 ⑥网络广播风暴详情 ↗
68. 某大楼干线子系统采用多模光纤布线,施工完成后,发现设备间子系统到楼层配线间网络丢包严 重,造成该故障可能的原因是 (68) 。详情 ↗
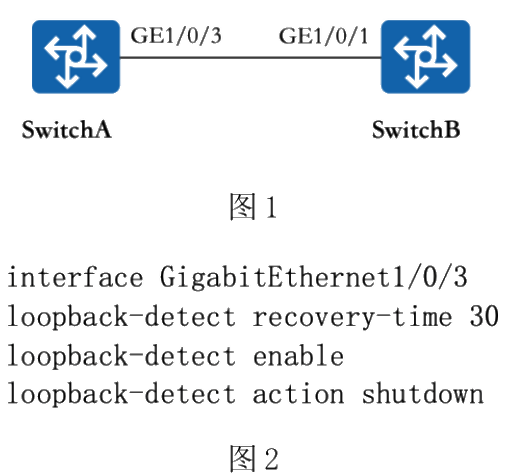
69. 如图 1 所示,某网络中新接入交换机 SwitchB,交换机 SwitchB 的各接口接入网线后,SwitchA 的 GE1/0/3 接口很快就会处于 down 状态,拔掉 SwitchB 各接口的网线后(GE1/0/1 除外),SwitchA 的 GE1/0/3 接口很快就会恢复到 up 状态,SwitchA 的 GE1/0/3 接口配置如图 2 所示,请判断造成该故障原因可能是(69)。详情 ↗
70. 革数据中心中配 2 台核心交换机 CoreA 和 CoreB,并配置 VRRP 协议实现冗余,网络管理员例行检 查时,在核心交换机 CoreA 上发现内容为"The state of VRRP changed from master to other state “的告警日志。经过分析,下列选项中不可能的原因是 (70) 。详情 ↗
71. Secure Shell (SSH) is a cryptographic network protocol for operating network services securely over an (71) network, Typical applications include remote command-line, login, and remote command execution, but any network service can be secured with SSH. The protocol works in the (72) model, which means that the connection in established by-the SSH client connecting to the SSH server. The SSH client drives the connection setup process and uses public key cryptography to verify the (73) of the SSH server. After the setup phase the SSH protocol uses strong (74) encryption and hashing algorithms to ensure the privacy and integrity of the data that is exchanged between the client and server. There are several options that can be used for user authentication. The most common ones are passwords and (75) key authentication.详情 ↗
72. Secure Shell (SSH) is a cryptographic network protocol for operating network services securely over an (71) network, Typical applications include remote command-line, login, and remote command execution, but any network service can be secured with SSH. The protocol works in the (72) model, which means that the connection in established by-the SSH client connecting to the SSH server. The SSH client drives the connection setup process and uses public key cryptography to verify the (73) of the SSH server. After the setup phase the SSH protocol uses strong (74) encryption and hashing algorithms to ensure the privacy and integrity of the data that is exchanged between the client and server. There are several options that can be used for user authentication. The most common ones are passwords and (75) key authentication.详情 ↗
73. Secure Shell (SSH) is a cryptographic network protocol for operating network services securely over an (71) network, Typical applications include remote command-line, login, and remote command execution, but any network service can be secured with SSH. The protocol works in the (72) model, which means that the connection in established by-the SSH client connecting to the SSH server. The SSH client drives the connection setup process and uses public key cryptography to verify the (73) of the SSH server. After the setup phase the SSH protocol uses strong (74) encryption and hashing algorithms to ensure the privacy and integrity of the data that is exchanged between the client and server. There are several options that can be used for user authentication. The most common ones are passwords and (75) key authentication.详情 ↗
74. Secure Shell (SSH) is a cryptographic network protocol for operating network services securely over an (71) network, Typical applications include remote command-line, login, and remote command execution, but any network service can be secured with SSH. The protocol works in the (72) model, which means that the connection in established by-the SSH client connecting to the SSH server. The SSH client drives the connection setup process and uses public key cryptography to verify the (73) of the SSH server. After the setup phase the SSH protocol uses strong (74) encryption and hashing algorithms to ensure the privacy and integrity of the data that is exchanged between the client and server. There are several options that can be used for user authentication. The most common ones are passwords and (75) key authentication.详情 ↗
75. Secure Shell (SSH) is a cryptographic network protocol for operating network services securely over an (71) network, Typical applications include remote command-line, login, and remote command execution, but any network service can be secured with SSH. The protocol works in the (72) model, which means that the connection in established by-the SSH client connecting to the SSH server. The SSH client drives the connection setup process and uses public key cryptography to verify the (73) of the SSH server. After the setup phase the SSH protocol uses strong (74) encryption and hashing algorithms to ensure the privacy and integrity of the data that is exchanged between the client and server. There are several options that can be used for user authentication. The most common ones are passwords and (75) key authentication.详情 ↗